Managed External Attack Surface Management (EASM) that continuously monitors your organisation from the outside in. Real security analysts investigate meaningful findings and help you understand what needs attention.
24×7×365 monitoringHuman investigationFrom £350/month per company, ex VAT
ConnectProtect® Insight
Managed vulnerability management
Turn vulnerability findings into clear next steps.
Managed vulnerability scanning and management that continuously identifies, prioritises, reports and tracks vulnerabilities across your agreed technology environment, so you know what needs attention first.
A list of 2,000 vulnerabilities isn’t 2,000 useful answers.
New devices appear, software changes, configurations shift and new CVEs are discovered every day. An assessment carried out once or twice a year can’t tell you everything you need to know today.
Finding vulnerabilities is only the first step. Someone still needs to know which systems are affected, which issues are most serious, where to focus first and what has already been addressed.
What Insight delivers
From vulnerability scanning to vulnerability management.
01
Continuous internal and external scanning
Identify vulnerabilities inside your environment and weaknesses visible from outside, and keep scanning as your technology changes.
02
Asset visibility and CVE reporting
See which assets are assessed, where vulnerabilities exist and the associated CVE information.
03
Prioritisation
Separate vulnerabilities that need immediate attention from lower-priority findings, so teams know what to fix first.
04
Progress tracking
See what’s new, what’s outstanding, what’s been addressed and whether your exposure is reducing over time.
05
Reporting for every audience
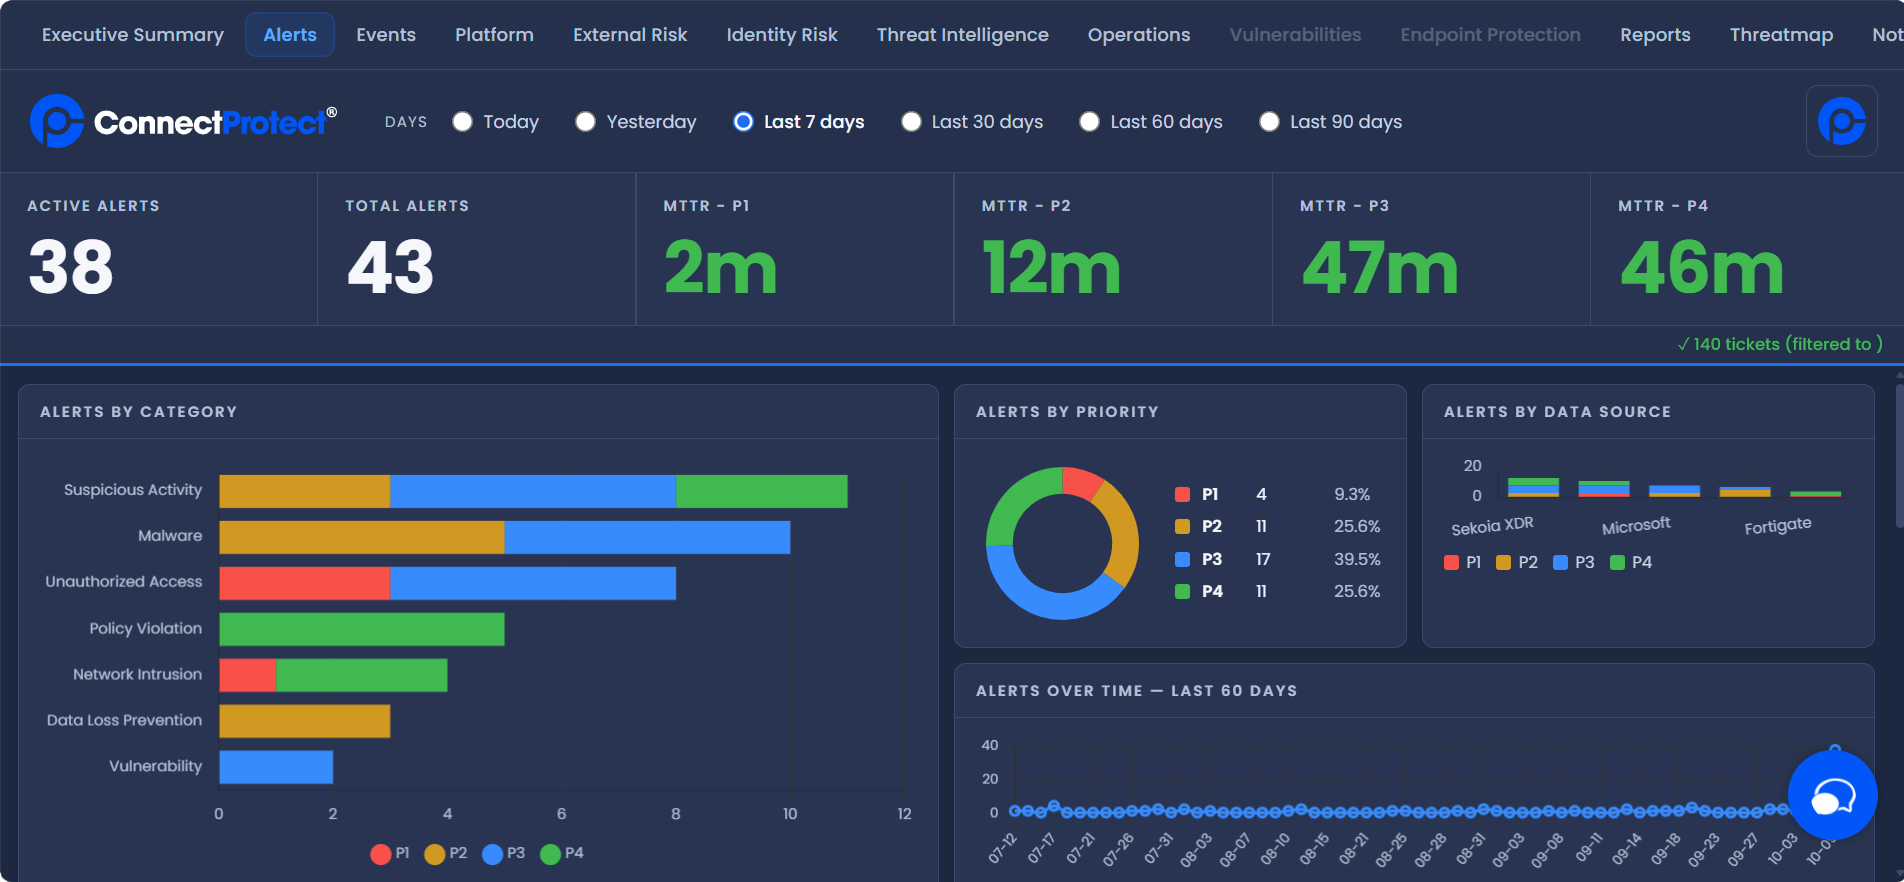
Technical and executive dashboards, PDF and PowerPoint reporting, the ConnectProtect app and regular service reviews.
The underlying RoboShadow platform supports continuous scanning across internal and external environments, including vulnerability identification and CVE reporting. RoboGuard supports daily automated scanning.
How it works
We find it. We show you. You fix it.
01
Scan
Continuously scan the agreed technology environment for vulnerabilities and security weaknesses.
02
Identify
Determine which assets, systems and applications have known vulnerabilities.
03
Prioritise and report
Show what needs attention first, with detail for IT and a clear view for leadership.
04
Track and scan again
Monitor what remains outstanding and what has been addressed, then reassess.
Remediation stays with your team or partner
Insight identifies, prioritises, reports and tracks vulnerabilities. It does not perform remediation or patching.
Remediation is carried out by the people who operate the technology: your internal IT team, MSP or IT provider, application provider, infrastructure team, or cloud or hosting partner.
They decide how and when to remediate, allowing for testing, dependencies, maintenance windows and change control.
Fit and differentiation
Built to work with your IT partner.
If you already have an MSP or IT provider, Insight doesn’t replace them. It gives them better information about what needs attention, then scans again and tracks the result.
ConnectProtect
Find
Prioritise
Report
Track
Your IT team or partner
Assess
Plan
Patch
Remediate
Who it suits
Organisations that need continuous scanning, clear asset visibility, useful prioritisation, good reporting, ongoing tracking and people to speak to, without buying into a large enterprise vulnerability management platform.
Related product
Want a continuous outside-in view of your exposure, with analysts investigating findings? Horizon monitors your external attack surface.
Build continuous visibility of the suppliers and third parties your organisation depends on. Start with one critical supplier or build visibility across your wider supply chain.