Keep watch over the devices your business depends on.
Antivirus, Endpoint Detection and Response (EDR) and anti-ransomware protection for your laptops, desktops and servers, monitored 24×7×365 by the ConnectProtect Security Operations Centre. Real analysts investigate meaningful activity and respond when action is required.
AntivirusEDRAnti-ransomware24×7×365 SOC monitoringHuman investigation & response
Why it matters
Installing endpoint software is one thing. Having someone watching it is another.
Laptops, desktops and servers are where your people work, your applications run and your business information is accessed. They’re also where cyber attacks can happen.
Security alerts don’t stop at 5pm, and an attack won’t wait for someone from IT to be at their desk. Many organisations don’t have, or don’t want, an internal team watching security activity around the clock.
What Core delivers
Layers of protection, with people behind them.
Protect
Antivirus
Helps protect devices against viruses, malware and known malicious threats.
Detect
Endpoint Detection and Response
Deeper endpoint visibility and behavioural detection to identify suspicious activity, giving analysts the information to investigate what happened.
Defend
Anti-ransomware
Dedicated capabilities designed around ransomware activity, where ConnectProtect’s supplied technology is used.
Monitor
24×7×365 SOC
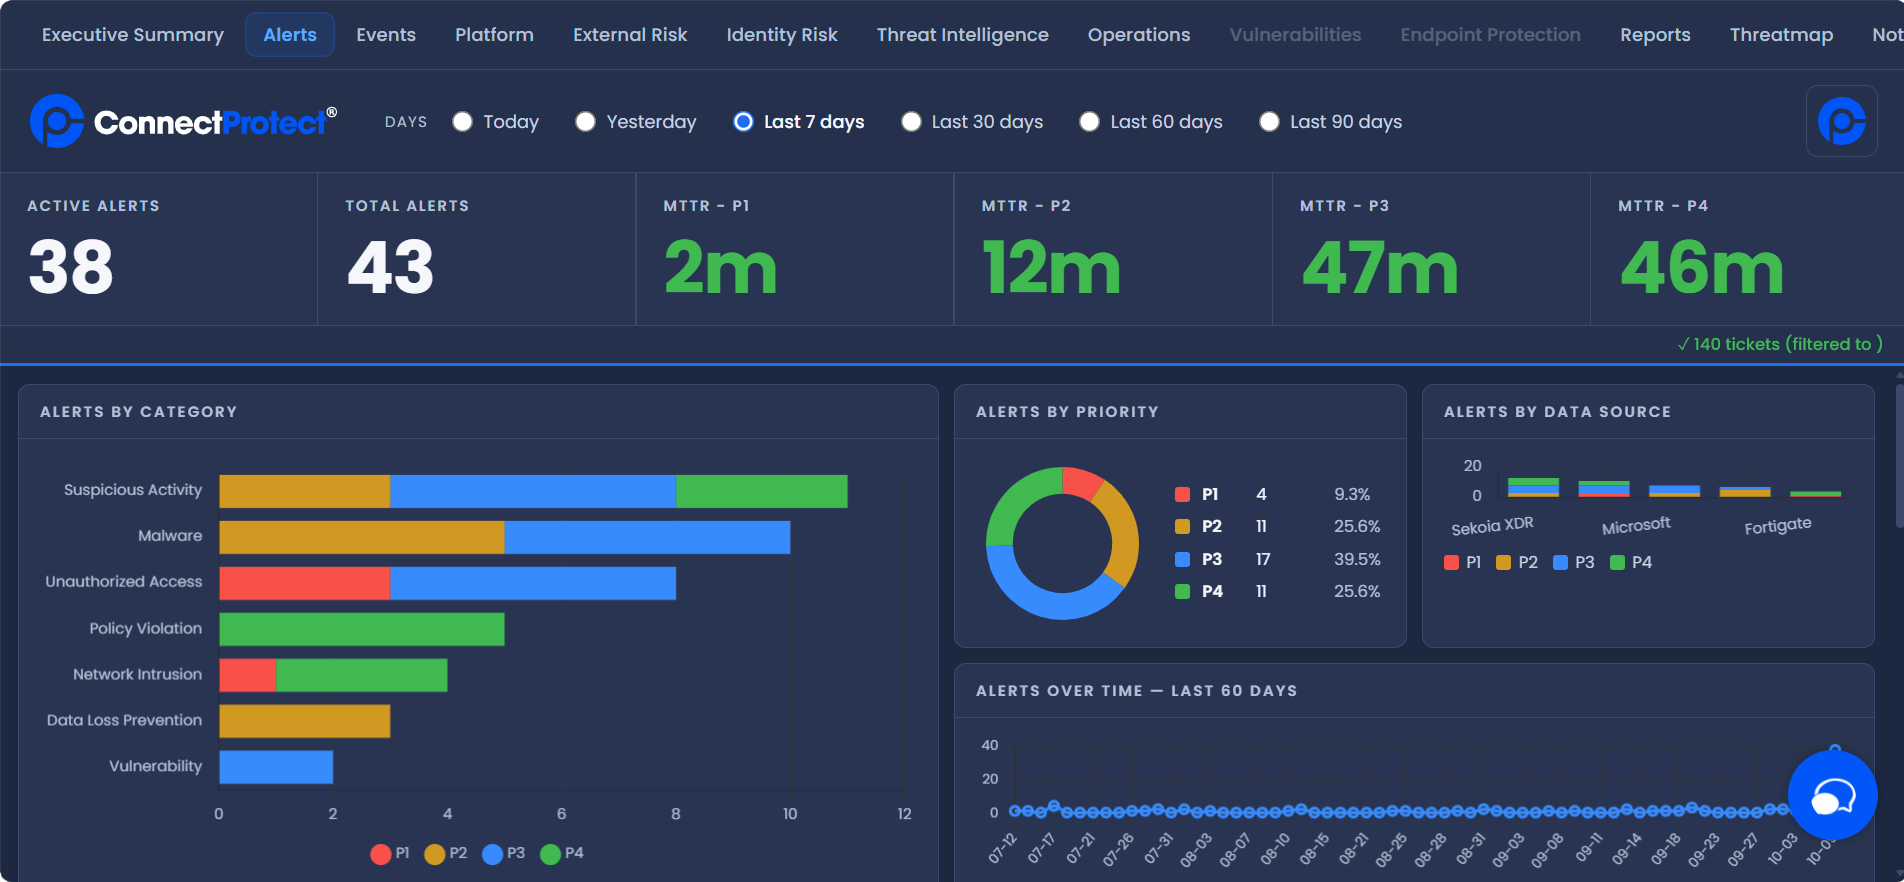
Continuous monitoring of endpoint security activity, so your IT team doesn’t have to watch another console.
Investigate & respond
Human analysts
AI and automation help surface and prioritise activity. Real analysts add context and judgement, and act within the agreed service.
How it works
From detection to response.
01
Monitor
Endpoint security telemetry is continuously brought into ConnectProtect.
02
Detect
Security technologies identify suspicious activity and potential threats.
03
Investigate
Security analysts add context and determine what is happening.
04
Respond
Appropriate response is taken according to the agreed service and available technology.
Service boundaries
- Response is carried out within the agreed service and depends on the technology available.
- Existing EDR can be monitored only where ConnectProtect supports that platform.
- Anti-ransomware capabilities apply where ConnectProtect’s supplied technology is used. No service can guarantee that attacks will never occur.
Fit and differentiation
Use the EDR you have, or let us provide it.
Already have EDR? Keep it.
Where your existing EDR platform is supported, Core can ingest and monitor its telemetry and add 24×7×365 monitoring, investigation and response. No unnecessary rip-and-replace, and no second agent on your devices.
Don’t have EDR? We’ll provide it.
ConnectProtect can provide the antivirus, EDR and anti-ransomware capabilities Core requires. We provide the technology, connect it and monitor it.
Who Core is for
- IT teams that don’t want to monitor security alerts around the clock
- Organisations looking for managed endpoint security or managed EDR
- Companies that want 24/7 endpoint monitoring without building an internal SOC
- Organisations with supported EDR that want managed monitoring and human expertise
- Businesses strengthening endpoint and ransomware protection
Related product
Want monitoring beyond your endpoints? Unity connects your supported identity, network, cloud and application security tools to the same SOC.
Contract options
Try it. Stay flexible. Or commit and save.
One company. One simple price.
Your devices don’t stop working. Neither should your protection.
Use the EDR technology you’ve already invested in, or let ConnectProtect provide it. Start with a free trial, then choose a rolling contract or a 12-month commitment.
