Their risk could become your risk
24x7x365 monitoring
Human investigation
External visibility
From £350/month per company
No size brands
No surprises
24x7x365 monitoring
Human investigation
External visibility
From £350/month per company
No size brands
No surprises
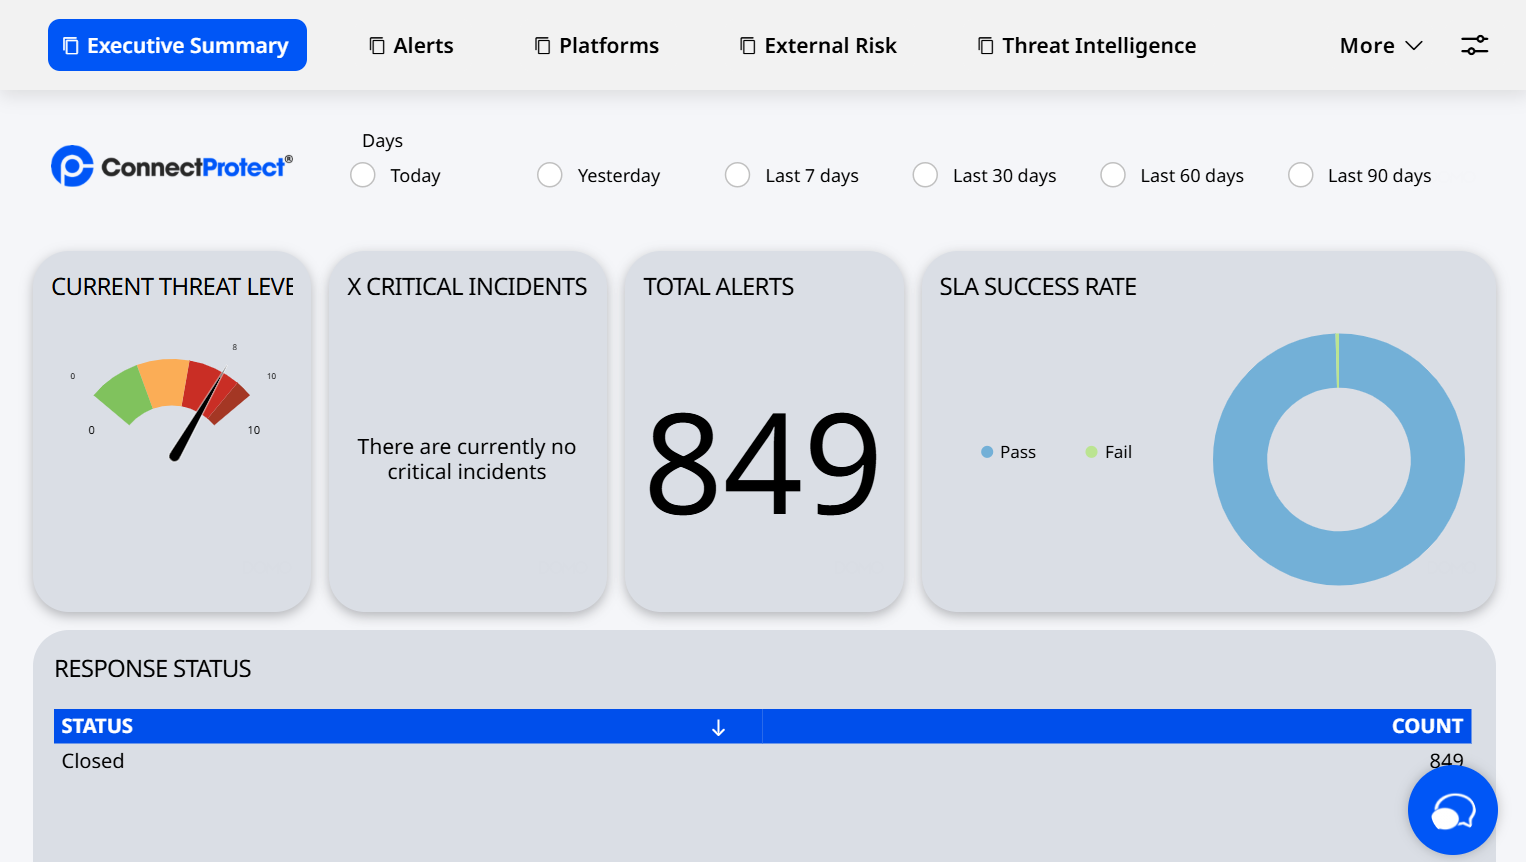
Continuous Third-Party Cyber Risk Management that monitors the external cyber security posture of the suppliers and third parties your organisation depends on.
ConnectProtect Realm gives you continuous supplier cyber risk monitoring, helping you understand changes in your suppliers’ external security posture, identify potential vulnerabilities and exposures, and know where attention may be required.
Monitor one critical supplier or build visibility across your wider supply chain.
Your cyber security doesn't stop with you.
You can control your security. You can't control theirs.
Your suppliers, technology providers and third parties may hold your data, access your systems, provide critical technology or deliver services your organisation depends on.
If one of those organisations is compromised, the consequences may not stop with them. That’s why Third-Party Cyber Risk Management matters.
ConnectProtect Realm extends your security visibility beyond your own organisation, helping you continuously monitor the external cyber security posture of the suppliers and third parties that matter to your business.
Because their cyber risk could become your risk.
See the businesses your business depends on.
Traditional third-party risk management often relies on questionnaires, assessments and periodic reviews. They’re useful. But they only tell you what was true when the assessment happened. Realm keeps watching.
Monitor your suppliers
Choose the suppliers, vendors and third parties that matter most to your organisation.
Understand their external security posture
See what can be observed about their cyber security position from outside their organisation.
Identify potential risk
Surface potential vulnerabilities, exposures and changes that could indicate increased cyber risk.
Know what has changed
Continuous monitoring helps you see changes between formal supplier security assessments.
Don't just ask your suppliers if they're secure.
See what you can observe for yourself.
Supplier questionnaires and security assessments have an important place in Third-Party Risk Management (TPRM). But cyber security changes.A supplier can complete a security questionnaire today and have a new vulnerability tomorrow.
Infrastructure can change. Services can be exposed. Credentials can become compromised. Security configurations can change.
Realm adds continuous external supplier monitoring to your existing third-party risk management process. Instead of relying solely on what a supplier tells you, you can also maintain visibility of what can be observed externally.
What was secure when you asked them? What’s secure now? That’s the difference continuous monitoring can make.
Their exposure. Your visibility.
Supplier cyber risk monitoring
Monitor selected suppliers and third parties from an outside-in cyber security perspective.
Continuous third-party monitoring
Realm continuously monitors your selected supplier domains, helping identify changes in their external cyber security posture.
Supplier security monitoring
Gain ongoing visibility rather than relying entirely on point-in-time supplier security assessments.
Supplier vulnerability monitoring
Identify potential externally observable vulnerabilities and weaknesses associated with monitored suppliers.
Supplier comparison
Compare selected suppliers to help understand where potential risk may be greater and where attention may be required.
Human investigation
Technology identifies signals. Our security analysts help you understand what they mean.
From signal to supplier conversation.
Realm isn’t designed to become another dashboard that your team has to spend hours monitoring. It is designed to help you identify where you need to look and who you may need to talk to.
01 -
Monitor
Select the suppliers and third parties that matter to your organisation.
02 -
Detect
Realm continuously monitors their external cyber security posture for changes and potential exposure.
03 -
Understand
Review findings and understand which suppliers or issues may require greater attention.
04 -
Engage
Use the information to have better-informed conversations with suppliers and support your wider third-party risk management process.
Less chasing. Better conversations.
Less assumption. More visibility.
Who could affect us?
Which suppliers, vendors and third parties could have a meaningful impact on our organisation?
What can we see?
What does their external cyber security posture look like from outside their organisation?
What's changed?
Has their external attack surface or security posture changed since the last assessment?
Who needs our attention?
Which suppliers should we be investigating or talking to?
You don't need to monitor everyone.
Start with who matters.
You probably don’t need to continuously monitor every organisation your business has a relationship with.
Start with the suppliers whose compromise, disruption or cyber incident could have the greatest impact on your organisation.
Consider suppliers that:
- hold your data
- access your systems
- provide critical technology
- provide essential services
- support important business processes
- could significantly affect your customers
- could create regulatory or reputational consequences if compromised
Start with one critical supplier. Build your Realm as your requirements grow.
Supplier risk shouldn't need another spreadsheet.
Managing third-party cyber risk can quickly become a combination of questionnaires, spreadsheets, annual reviews and chasing suppliers for answers.
Realm gives you another layer of visibility.
Continuous monitoring
Monitor your selected suppliers between formal assessments.
External visibility
Understand what can be observed about their cyber security posture from outside.
Risk prioritisation
Focus your attention where potential risk appears greatest.
Human expertise
ConnectProtect analysts can investigate meaningful findings and provide context.
Better supplier conversations
Use current external intelligence to support conversations about potential cyber security concerns.
Built for everyone responsible for supplier risk.
01 -
IT & Security
Gain visibility of cyber risk beyond your own organisation.
02 -
Risk & Compliance
Add continuous external monitoring to your existing third-party risk management processes.
03 -
Procurement
Bring cyber security information into supplier selection and ongoing supplier reviews.
04 -
Leadership
Understand the potential cyber risks associated with organisations your business depends upon.
05 -
Cyber Insurance
Support your wider approach to identifying and managing third-party cyber risk.
Your supplier was secure when you asked them.
What about today?
This is one of the fundamental problems with point-in-time supplier assessments. A supplier may have passed your assessment six months ago.
Since then:
- a new vulnerability may have emerged
- infrastructure may have changed
- a service may have become externally exposed
- credentials may have been compromised
- security configuration may have changed
Supplier cyber risk is dynamic.
Realm provides continuous supplier cyber security monitoring, helping you maintain visibility between formal assessments.
Technology plus human monitoring.
Not just another TPRM platform. Realm combines technology and external cyber risk intelligence with ConnectProtect’s human security expertise.
Continuous monitoring
Your suppliers don’t only get assessed when someone remembers to check.
Human oversight
Our security analysts can investigate meaningful findings and add context.
Clear information
Understand what has changed and why it may matter.
Risk prioritisation
Focus your attention on the suppliers and findings that deserve it.
Ongoing visibility
Build a continuous picture of supplier cyber risk over time.
Tell us who matters to your business. We'll help you keep watch.
Your supplier due diligence still matters.
Realm doesn’t replace your existing supplier security assessments.
Questionnaires, certifications, contractual controls, audits and other due diligence can all provide valuable information about a supplier’s security.
Realm complements them.
Traditional due diligence can tell you what a supplier says about its security controls. Realm helps you maintain visibility of what can be observed externally. Together, these approaches can give you a more complete picture of supplier cyber risk.
How do I know if my suppliers are secure?
You can’t rely on a single assessment to tell you what is happening today. Supplier security changes continuously.
Realm provides continuous external monitoring of selected suppliers, helping identify potential vulnerabilities, exposures and changes in external cyber security posture. That doesn’t mean Realm can guarantee a supplier is secure. It means you have another source of ongoing visibility to support better third-party risk decisions.
You don’t have to monitor your entire supply chain.
Start with your critical suppliers. Identify the organisations that could have the greatest impact on your business if they suffered a cyber incident.
Then bring them into your Realm.
1 critical supplier
Start small.
5 suppliers
Build visibility across your critical supplier group.
10 suppliers
Build wider supply-chain cyber risk visibility.
More than 10
Build a monitoring programme around your requirements.
Your supplier risk strategy should start with the organisations that matter most.
Start with one. Build your Realm.
Your supplier landscape is unique to your organisation. That’s why Realm allows you to start with the suppliers that matter most and expand over time. Start where your risk starts. Expand when you’re ready.
How much does Realm cost?
Cyber security pricing shouldn’t need to become more complicated as your business grows. Horizon has a simple, predictable price per company, regardless of company size. No employee bands. No complicated usage calculations. No surprises because you’ve recruited more people.
The simplicity of ConnectProtect shouldn’t stop at the technology.
One company. One simple price.
Cyber security pricing shouldn't need a calculator.
- No employee bands
- Price doesn't increase when headcount does
- No company-size tiers
- A simple price per company domain
- No long-term commitment required
- Choose Monthly Defender if flexibility matters
- No annual prepayment required
- Choose Annual Protector and pay monthly if preferred
- Price excludes VAT
Annual Protector
£350 / month
- Trusted annual protection for business continuity
- 12-month commitment
- Pay monthly or annually - the price stays the same
Monthly defender
£420 / month
- Consistent defense with no long‑term lock‑in
- Rolling monthly
- No long-term commitment
- Stay as long as Horizon makes sense for you
Horizon at a glance
Their business is part of your business.
Their cyber risk should be part of your security strategy.
Build continuous visibility of the suppliers and third parties your organisation depends on.
Start with one critical supplier or build visibility across your wider supply chain.