Find what needs fixing
Managed vulnerability scanning and vulnerability management that continuously identifies, prioritises, reports and tracks vulnerabilities across your technology environment.
Your technology changes every day. New devices appear. Software is installed. Applications are updated. Configurations change. New vulnerabilities are discovered. A vulnerability scan can tell you that weaknesses exist. But finding vulnerabilities is only the beginning.
What are you vulnerable to? Where is the vulnerability? How serious is it? What should you look at first? Who needs to deal with it? Has it been addressed? ConnectProtect Insight is designed to help answer those questions.
You can't fix what you don't know about.
Your vulnerability picture changes every day.
A vulnerability assessment carried out once or twice a year provides useful information. But your technology environment doesn’t stop changing once the assessment is complete. New systems are deployed. Software versions change. Applications are updated. Configuration changes are introduced. And new CVEs and vulnerabilities are discovered continuously.
That means yesterday’s vulnerability assessment may not tell you everything you need to know today.
Continuous vulnerability visibility.
The underlying RoboShadow platform supports continuous scanning across internal and external environments, including vulnerability identification and CVE reporting. RoboGuard supports daily automated scanning.
Your technology changes. Your vulnerability picture changes with it. So Insight keeps looking.
What is vulnerability management?
Finding vulnerabilities is only the first step.
A vulnerability scanner finds weaknesses. Vulnerability management is the ongoing process of identifying, understanding, prioritising, reporting and tracking those weaknesses so that the right people can deal with them.
That’s the difference between:
“We found 2,000 vulnerabilities.”
and:
“We know what needs attention first.”
Insight is designed around the second question. It continuously identifies vulnerabilities across the agreed environment, helps prioritise findings, provides useful reporting and tracks what happens over time.
Don't just find it. Understand it.
Scan. Identify. Prioritise. Report. Track. Scan again.
One of the biggest problems with vulnerability scanning is volume. A vulnerability scan can identify dozens, hundreds or even thousands of findings.
But a list of 2,000 vulnerabilities isn’t necessarily 2,000 useful answers.
Someone still needs to understand:
- Which systems are affected?
- Which vulnerabilities are most serious?
- Which assets matter most?
- Where should we focus first?
- What remains outstanding?
- What has already been addressed?
Don’t just give me a vulnerability list. Tell me where to focus.
Continuous vulnerability scanning.
Don't wait six months to discover what changed yesterday.
Traditional vulnerability assessments can provide a useful snapshot of your environment. But a snapshot becomes outdated as soon as your environment changes.
Insight provides ongoing vulnerability visibility so that newly discovered or newly introduced weaknesses can be identified rather than waiting for the next scheduled assessment.
Continuous vulnerability scanning helps answer:
- What’s new?
- What’s still vulnerable?
- What’s changed?
- What needs attention?
- Are we actually reducing our vulnerability exposure?
Scan → Identify → Prioritise → Report → Track → Repeat
Insight helps turn findings into priorities.
From vulnerability scanning to vulnerability management.
Scan
Continuously scan the agreed technology environment for vulnerabilities and security weaknesses.
Identify
Determine which assets, systems and applications have known vulnerabilities or issues requiring attention.
Prioritise
Help distinguish vulnerabilities that deserve immediate attention from findings that represent a lower priority.
Report
Give technical teams the information they need to investigate and remediate vulnerabilities, while providing clearer visibility for management and leadership.
Track
Monitor findings over time so you can understand what remains outstanding, what has been addressed and how your vulnerability position is changing.
Scan again
The process continues.
Find it. Then understand it.
A vulnerability without context is difficult to act on. Insight is designed to help turn technical vulnerability data into useful information.
For technical teams, that can mean visibility into:
- affected assets
- CVEs
- vulnerability severity
- vulnerability details
- affected systems
- outstanding findings
- remediation progress
- changes over time
For management and leadership, it means a clearer view of:
- overall vulnerability exposure
- priority areas
- progress
- outstanding risk
- changes in the environment
Technical enough for IT. Clear enough for everyone else. Vulnerability prioritisation matters. Not every vulnerability deserves the same response.
Your organisation may have a large number of vulnerabilities. That doesn’t mean every finding should be treated identically. Some vulnerabilities may affect critical systems. Some may be actively relevant to your environment. Some may require urgent attention. Others may represent a lower priority.
Insight helps your teams understand where to focus first.
The question isn’t: “How many vulnerabilities do we have?”
It’s: “Which vulnerabilities should we fix first?”
We find it. We show you. You fix it.
Built to work with your IT partner.
This is an important part of how Insight works. ConnectProtect Insight identifies vulnerabilities. It helps prioritise them. It reports them. It tracks them.
The actual remediation remains with the people responsible for operating the technology.
- your internal IT team
- your MSP or IT service provider
- an application provider
- your infrastructure team
- a cloud or hosting partner
- another specialist technology provider
And there is a reason for that. Patching and remediation can affect applications, systems and business processes. Updates may need testing. Systems may have dependencies. Maintenance windows may be required. Business-critical applications may need careful change control. The people responsible for operating that technology should therefore decide how and when a vulnerability is remediated.
ConnectProtect identifies. Your team or technology partner remediates.
Insight doesn’t need to take over your remediation work.
If you already have an MSP, IT provider or technology partner, ConnectProtect isn’t there to replace them. It’s actually quite the opposite.
Insight can give your technology partner better information about what needs attention.
ConnectProtect
Find • Prioritise • Report • Track
Your IT team or partner
Assess • Plan • Patch • Remediate
Then ConnectProtect scans again and tracks the result.
We find it. They fix it. Together, we protect your business.
It’s: “Which vulnerabilities should we fix first?”
Don't just find vulnerabilities.
Track what happens next.
Finding a vulnerability once doesn’t tell you whether anything happened afterwards. That’s where vulnerability management becomes more useful than a simple vulnerability scan. Insight helps you understand vulnerabilities over time.
New
What has appeared?
Outstanding
What still needs attention?
Addressed
What has been dealt with?
Changed
How is the overall position developing?
This moves the conversation away from: “How many vulnerabilities do we have?”
and towards: “Are we actually reducing our vulnerability exposure?”
Before you patch, understand what needs attention.
Finding vulnerabilities is the start. Reducing them is the goal. Know what needs patching.
Patch management and vulnerability management are related, but they are not the same thing. Vulnerability management tells you what needs attention. Patch management helps you fix it.
Insight is focused on identifying, prioritising, reporting and tracking vulnerabilities rather than performing the customer’s remediation work.
The responsibility is clear:
ConnectProtect identifies. Your team decides. Your team or partner remediates. Insight scans again.
This provides a continuous feedback loop between vulnerability identification and remediation.
One view for IT.
01 -
Another for everyone else.
Vulnerability information can become highly technical very quickly. Your IT team may need CVEs, affected assets, severity information and technical detail. The board probably doesn’t.
02 -
Technical dashboard
Give technical teams detailed vulnerability information they can investigate and act upon.
03 -
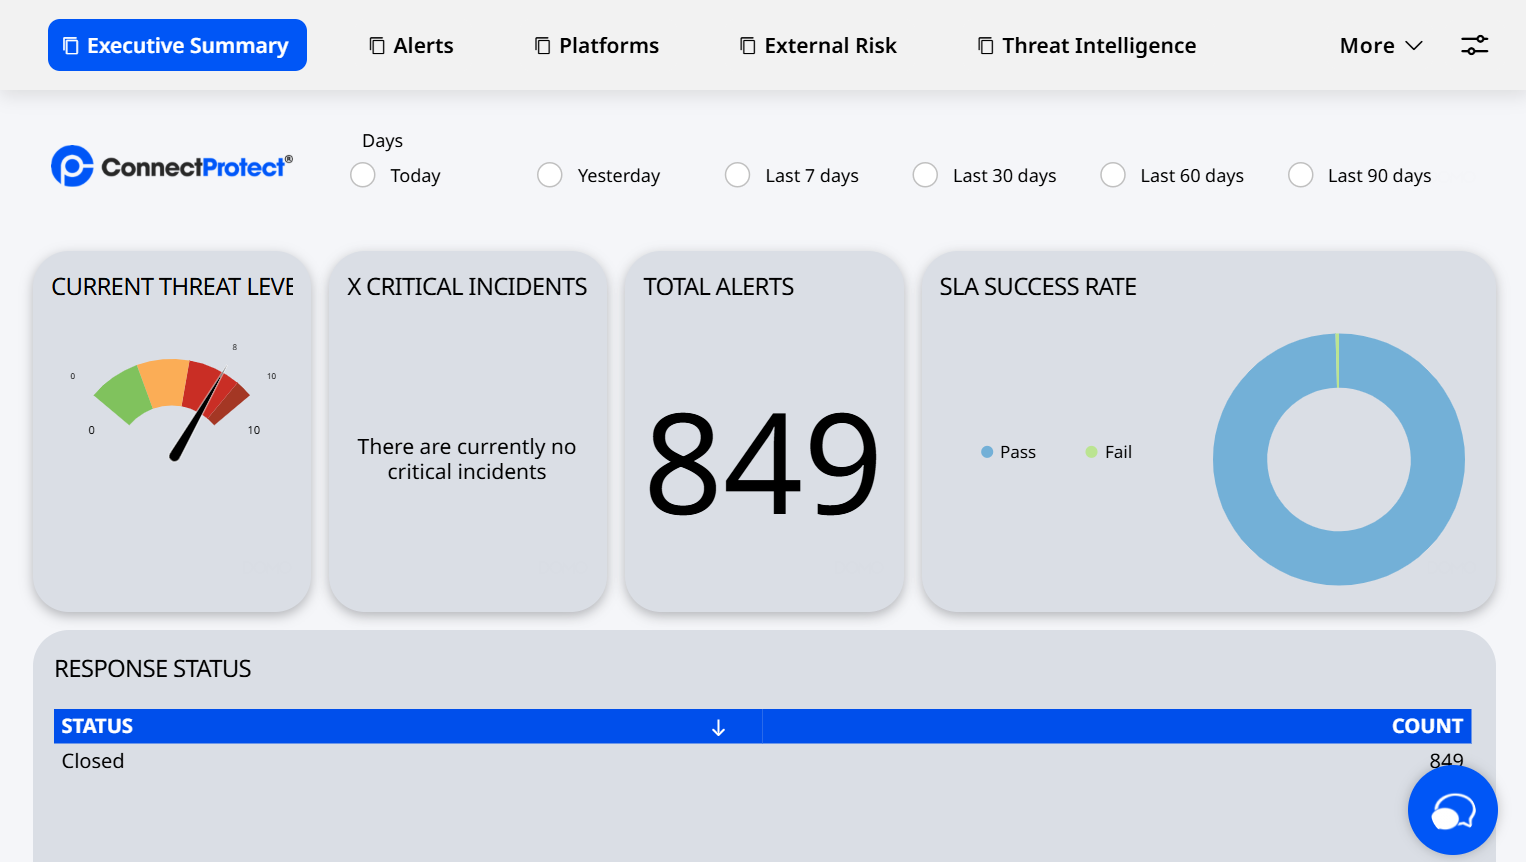
Executive dashboard
Give leadership a clearer picture of vulnerability exposure, priorities and progress without expecting them to interpret technical scan results.
04 -
PDF reporting
Create reports that can be shared with customers, colleagues, auditors and other stakeholders.
05 -
PowerPoint reporting
Bring vulnerability information directly into existing management, IT and board presentations.
06 -
ConnectProtect app
Receive relevant information and communicate with ConnectProtect away from the office.
07 -
Service reviews
Regular reviews help customers understand what has changed, where progress is being made and what continues to deserve attention.
Continuous visibility across your environment.
Internal & external vulnerability scanning.
Insight is designed to provide vulnerability visibility across agreed areas of your technology environment.
Internal vulnerability scanning
Identify vulnerabilities affecting systems and technology within your internal environment.
External vulnerability scanning
Understand vulnerabilities and exposed weaknesses visible from outside your organisation.
Asset visibility
Understand which assets are being assessed and where vulnerabilities exist.
CVE reporting
Identify known vulnerabilities and associated CVE information.
Continuous assessment
Continue scanning as your technology environment changes.
Ongoing tracking
Monitor whether vulnerabilities remain outstanding or have been addressed.
Don't guess.
Organisations often know they need to improve their cyber security. The difficult part is knowing where to start.
Insight can help answer practical questions such as:
- How do I know if my systems are vulnerable?
- How do I find vulnerabilities in my network?
- How do I find vulnerabilities in my business?
- How do I check company computers for vulnerabilities?
- How do I identify vulnerable software?
- How often should I vulnerability scan?
- How do I know what needs patching?
- Which vulnerabilities should I fix first?
- How do I track vulnerabilities?
- How do I reduce vulnerabilities?
These are not simply technical questions. They are business questions.
What needs fixing? Insight helps you find out.
A scan should lead somewhere.
Vulnerability scanning for organisations that want more than a report.
A vulnerability scanning service that simply produces a report leaves someone else to work out what it means.
Insight goes further. It provides a continuous cycle of:
Identification • Prioritisation • Reporting • Tracking • Reassessment
That gives your organisation a clearer picture of whether vulnerability exposure is improving over time.
Find it. Understand it. Prioritise it. Track it. Reduce it.
Enterprise vulnerability visibility.
Without the enterprise-sized bill.
Tenable, Qualys and Rapid7 offer highly capable vulnerability management platforms. But not every organisation needs a large enterprise vulnerability management ecosystem.
Some organisations simply need:
- continuous vulnerability scanning
- clear asset visibility
- vulnerability identification
- useful prioritisation
- good reporting
- ongoing tracking
- people they can speak to
- sensible pricing
Serious capability. Sensible pricing.
Enterprise vulnerability visibility. Without the enterprise-sized bill.
Why choose ConnectProtect Insight?
Continuous vulnerability management without unnecessary complexity.
Continuous scanning
Don’t rely solely on periodic vulnerability assessments.
Clear priorities
Understand which vulnerabilities deserve attention first.
Asset visibility
Know which systems and assets are affected.
CVE reporting
Understand known vulnerabilities and their associated information.
Ongoing tracking
See what is new, what remains outstanding and what has been addressed.
Human service
Have people you can speak to about your vulnerability position.
Works with your IT partner
Give your MSP or internal IT team better information without taking remediation work away from them.
Technical and executive reporting
Give each audience the information they need.
Sensible pricing
Get serious vulnerability visibility without automatically buying an enterprise-sized platform.
Horizon at a glance
FAQ
Find what needs fixing.
You can't fix what you don't know about.
Your technology changes. Your vulnerability picture changes. New vulnerabilities are discovered. New systems appear. Old vulnerabilities remain.
Insight keeps looking.
Scan. Identify. Prioritise. Report. Track. Repeat.
ConnectProtect Insight
Managed vulnerability scanning. Continuous vulnerability management. Clear priorities. Ongoing visibility.
We find it. We show you. You fix it.